Audit logs and SIEM streaming
When something goes wrong you need the timeline: who signed in from where, which token was issued, which agent asked for what and who approved it. LumoAuth records all of it, lets you search and export it, and streams it to the security tools your team already runs.
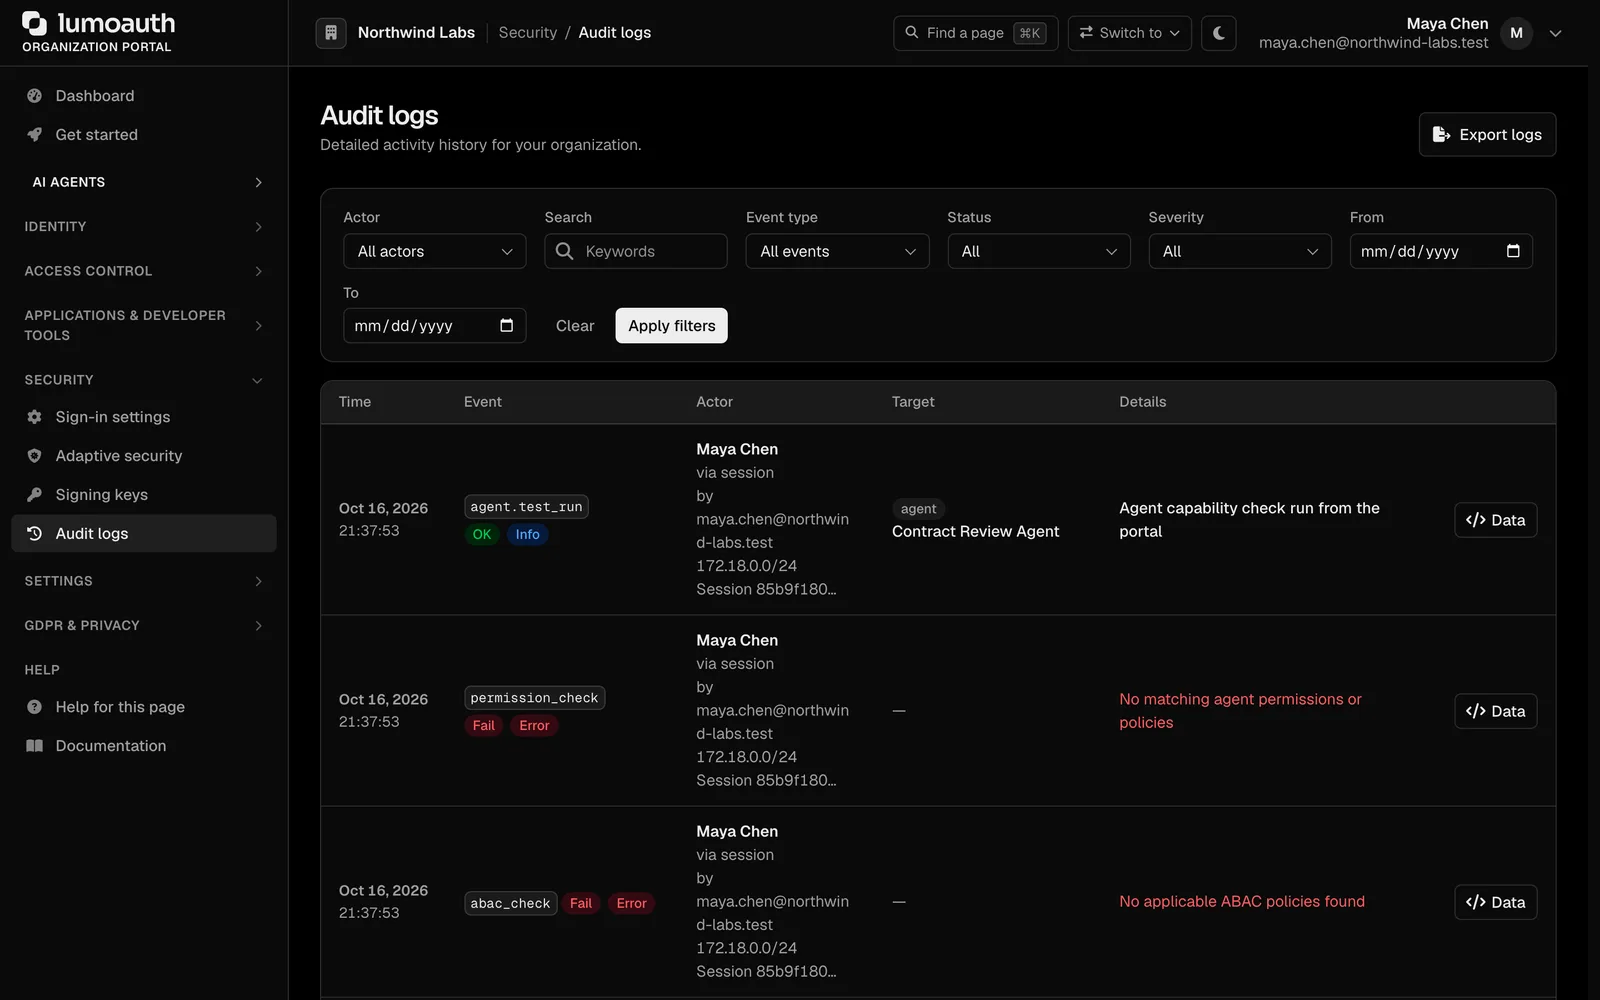
Auth logs scattered across services cannot answer "what happened?"
Reconstructing an account takeover from application logs takes days. Auditors want a complete trail with retention you can prove.
How LumoAuth solves it
A complete audit log
Sign-ins, failures, tokens, MFA, provisioning, settings changes, agent actions, approvals and privacy requests, each with actor, target, IP, geo, risk and a trace ID. Docs
Search, filter, export
Filter by user, event type, severity and time. Export CSV or JSON. Docs
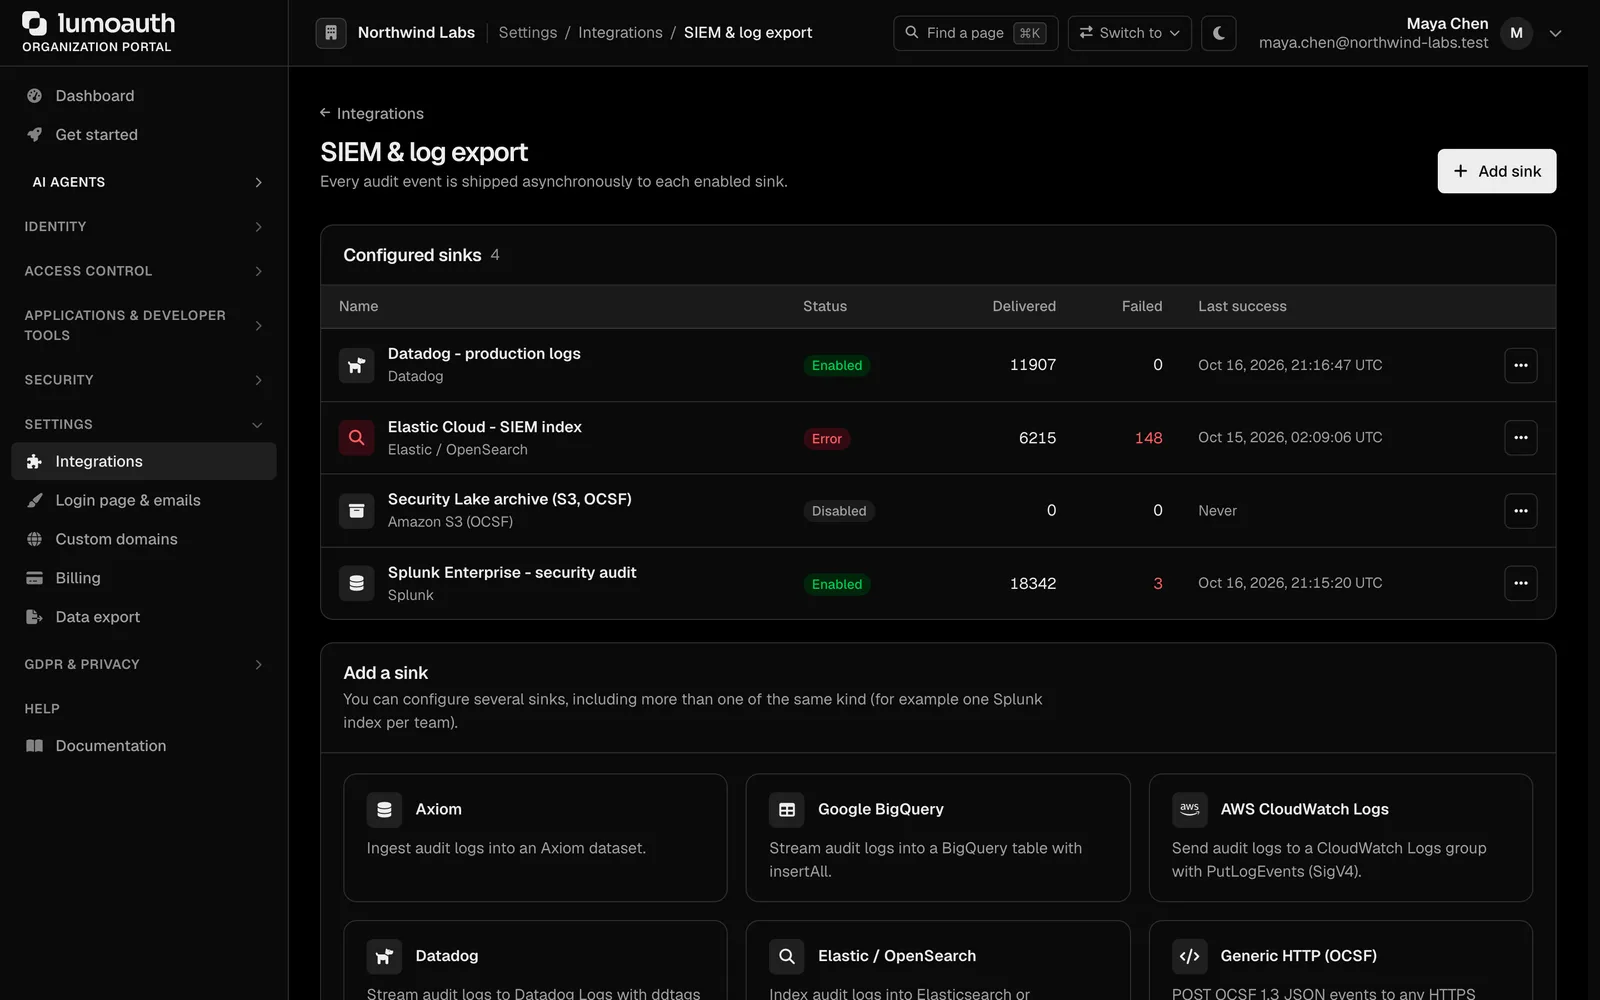
Stream to your SIEM
Splunk, AWS CloudWatch Logs, Microsoft Sentinel, Google SecOps, Elastic and OpenSearch, Sumo Logic, Datadog, Axiom, Honeycomb, Amazon S3 (OCSF), OpenTelemetry, any HTTPS endpoint, BigQuery and Snowflake. Docs
Alerts
High-severity events go straight to Slack, Teams, PagerDuty, Opsgenie or email. Docs
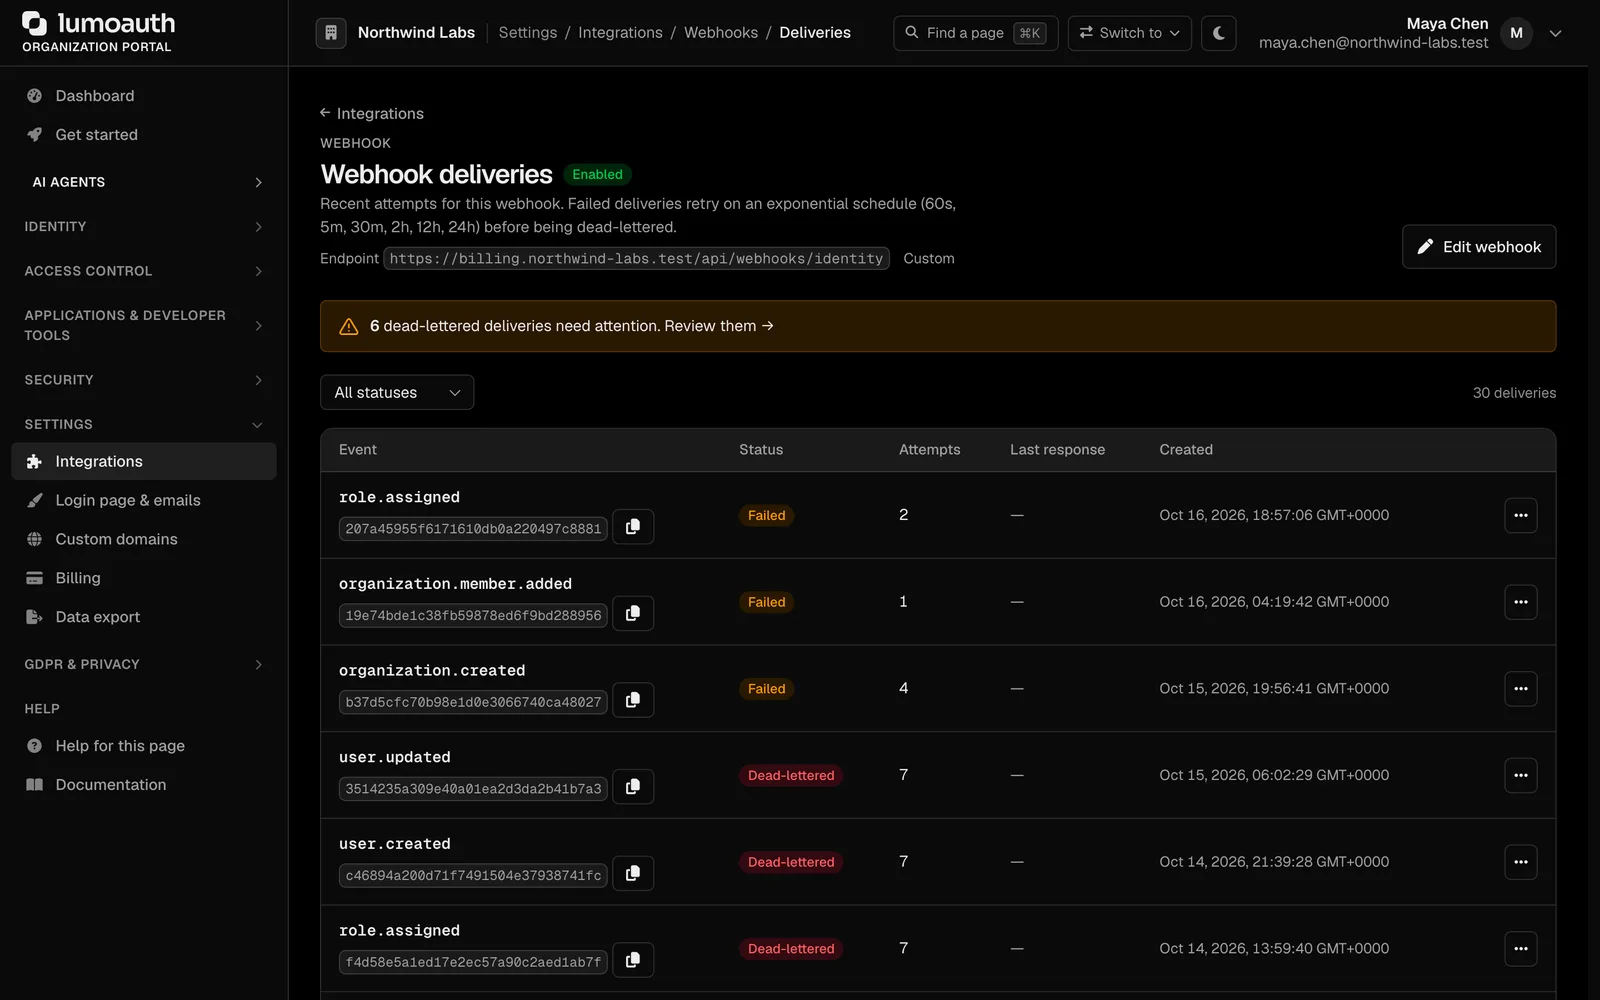
Webhooks
Signed deliveries for the events your own systems care about, with retries and a delivery history. Docs
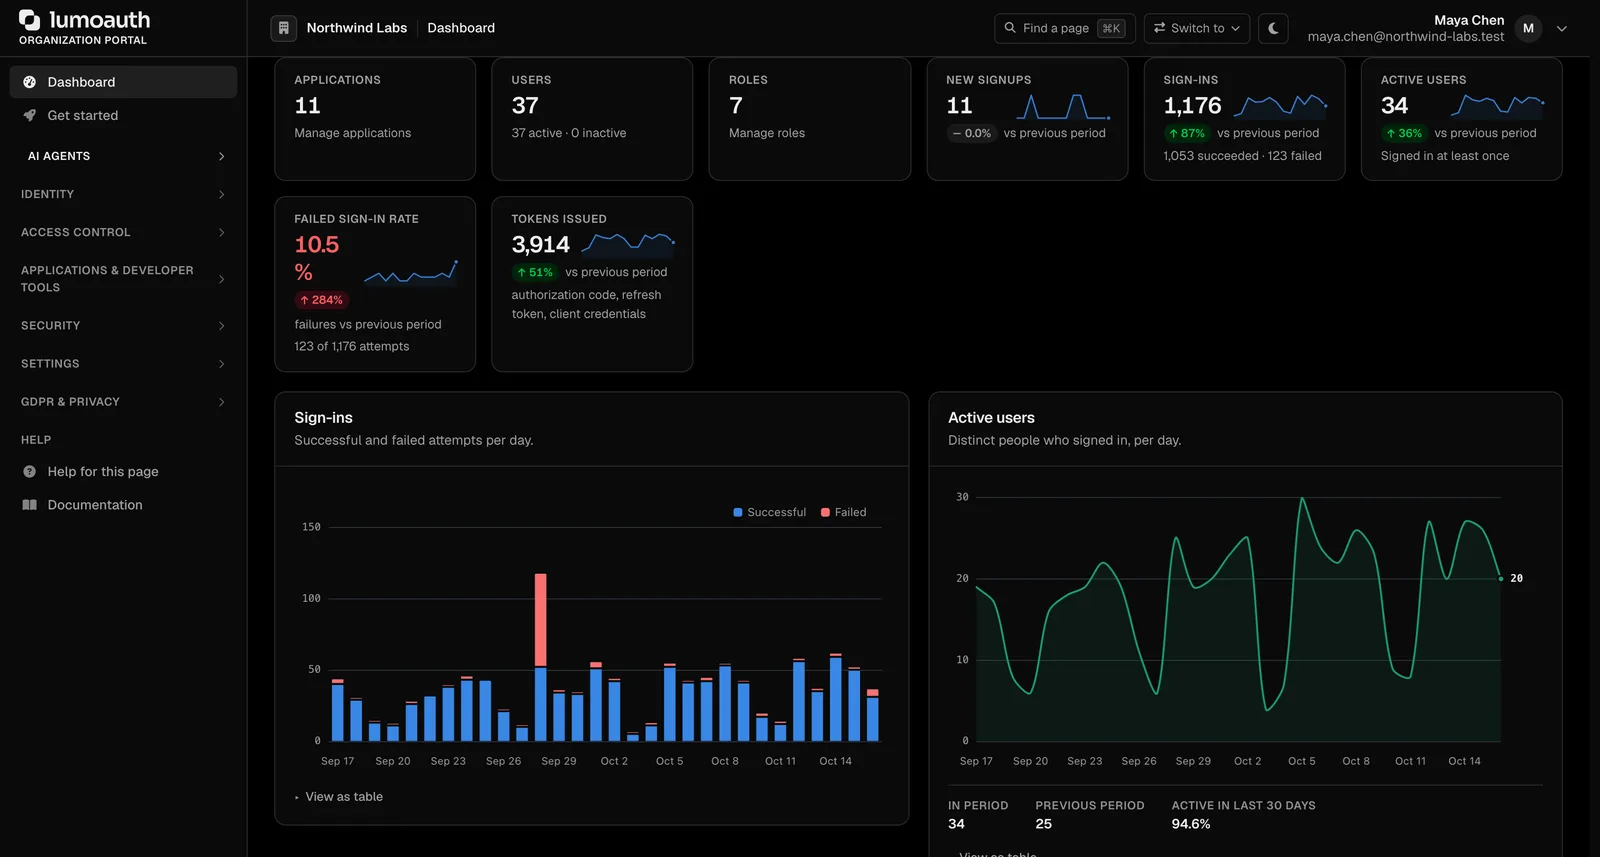
Dashboards and reports
Sign-ins, failures, methods, latency and agent activity on the dashboard; export reports as CSV or JSON. Docs
Setting it up
Pick a destination
Settings → Integrations → SIEM & log export.
Send a test event
Confirm it lands.
Set alert thresholds
Critical to PagerDuty, high to Slack.
Standards involved
Plain names on the left, the specification on the right. The full map is in the standards reference.
- Event schema
- OCSF for S3 and generic HTTPS
- Telemetry
- OpenTelemetry OTLP
- Trace correlation
- W3C Trace Context
Which plan you need
Audit retention is 3 days on Developer, 30 on Pro and 90 on Business, with a one-year option in the Audit & Compliance add-on. Audit export starts on Pro. Log streaming is included on Business (one stream, more at $99/month each) and in the Audit & Compliance add-on on Pro.
Documentation
Questions
Are logs tamper-evident?
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.