GDPR and privacy compliance
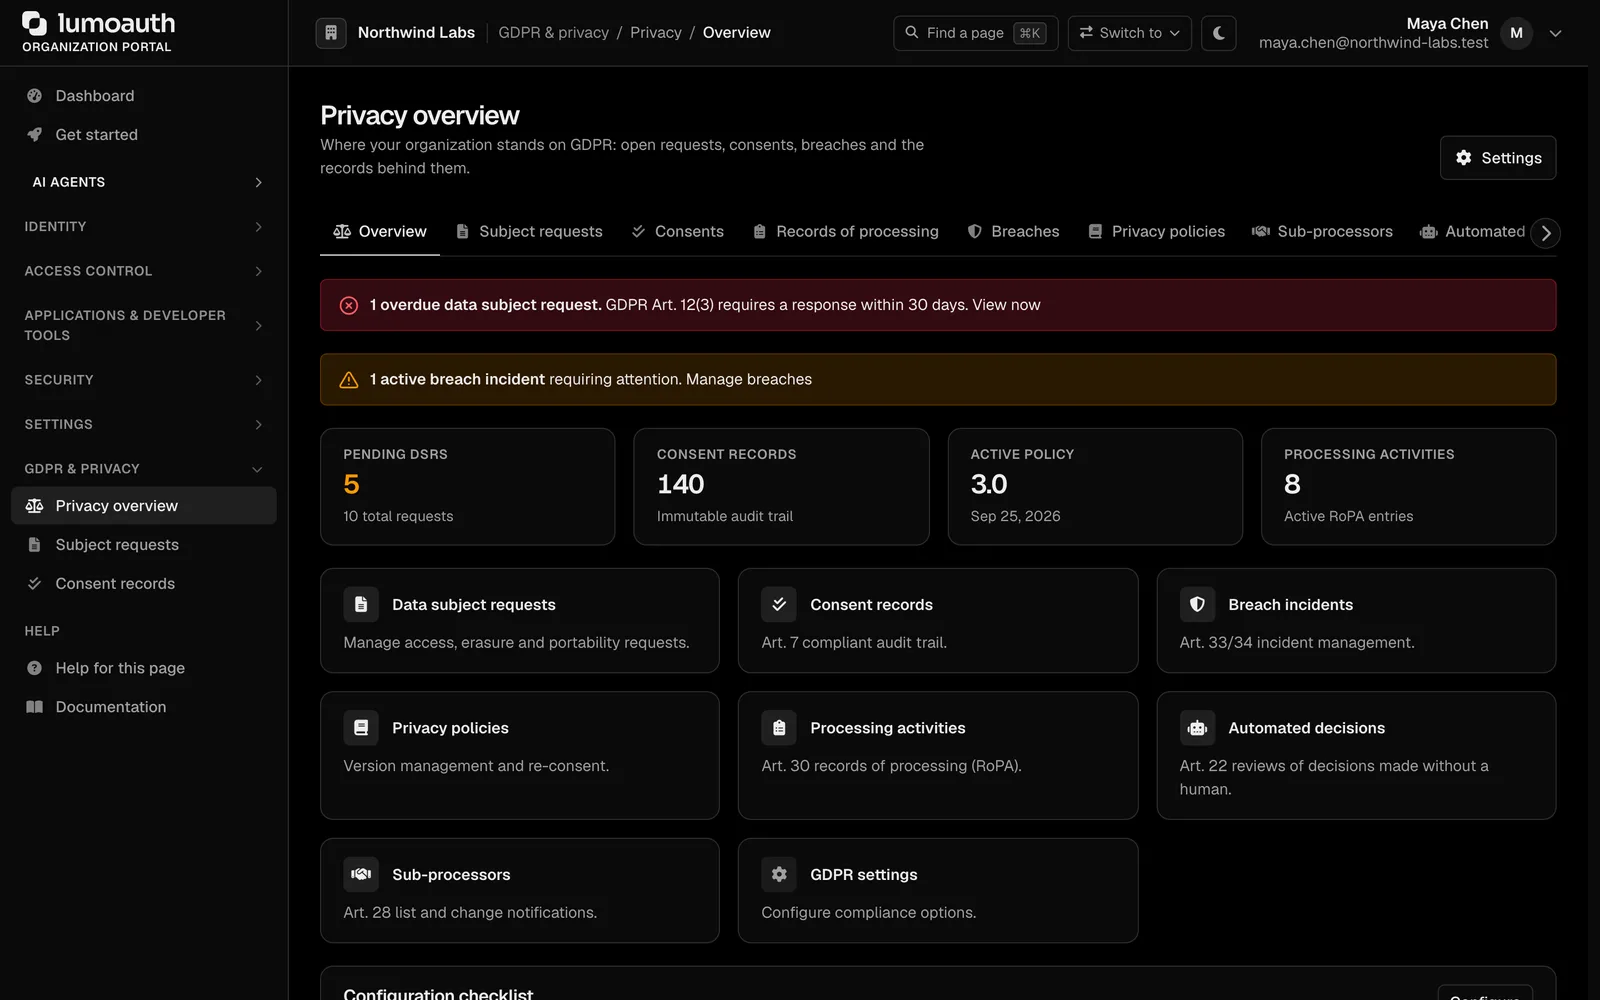
The identity system already knows what personal data you hold and who consented to what. LumoAuth turns that into the records a data-protection officer needs: self-service requests for users, versioned consent, records of processing activities, impact assessments and a breach workflow with the 72-hour clock built in.
Compliance by spreadsheet does not survive an audit
Deletion requests handled by hand get missed. Consent is "somewhere in the database". The record of processing is a document from two years ago.
How LumoAuth solves it
Data-subject requests
Access, correction, erasure, restriction, portability and objection, requested by users from their own account and tracked to completion. Docs
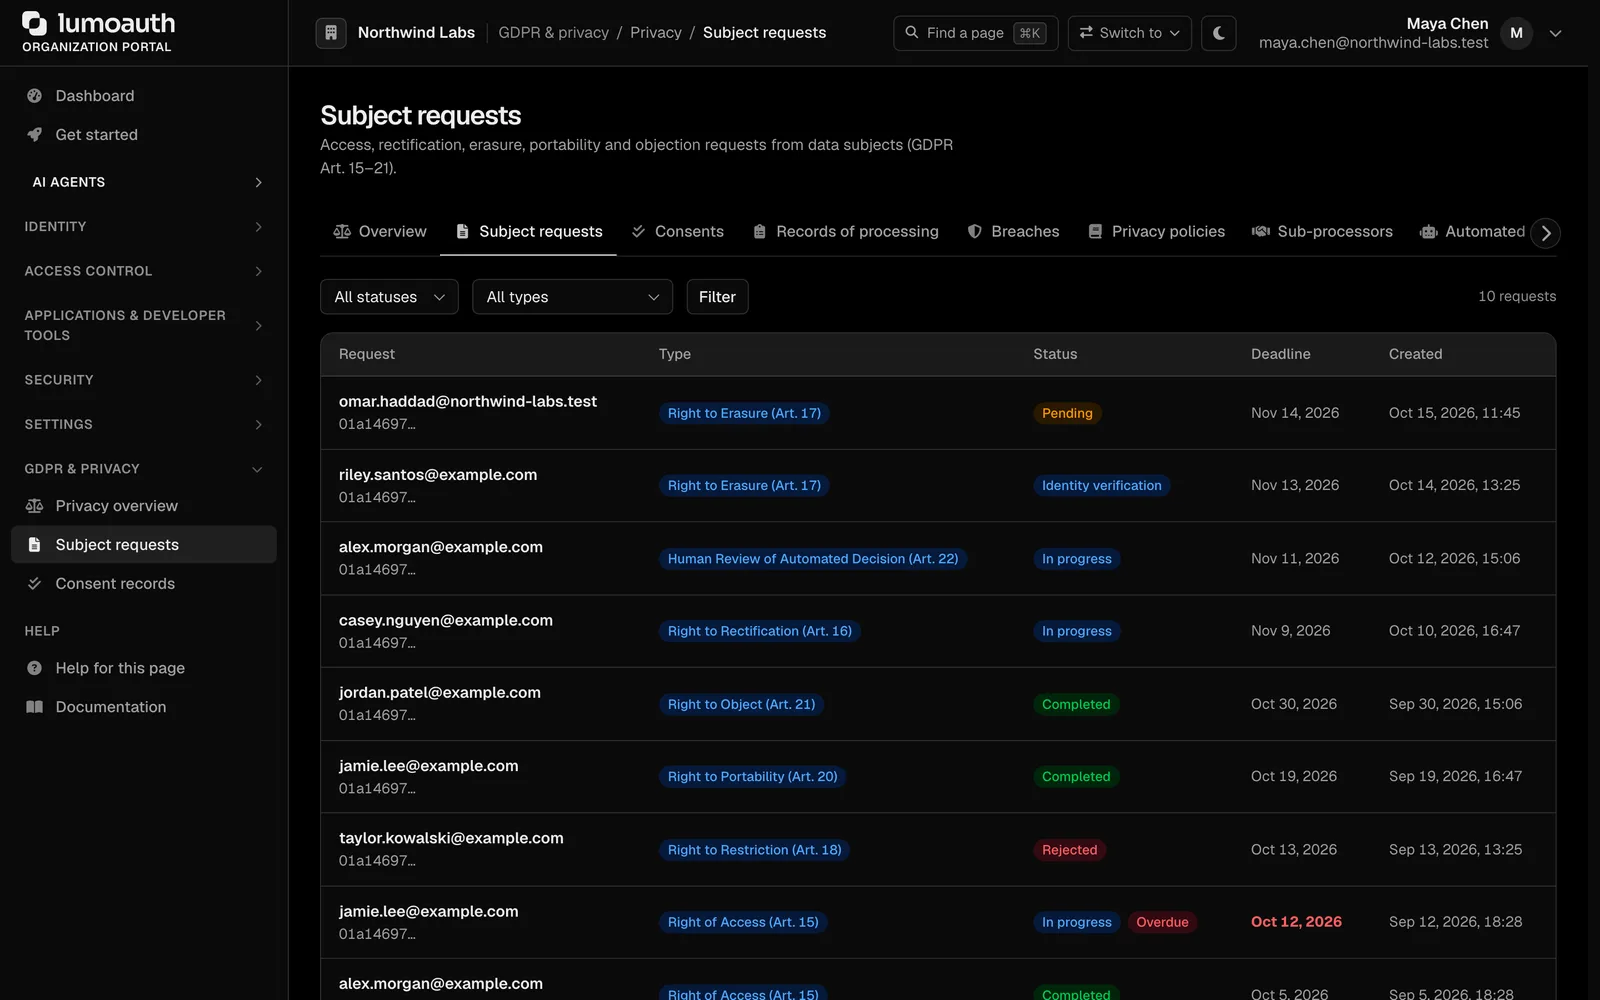
Consent records
Every consent is versioned, timestamped and revocable, with double opt-in for marketing. Docs
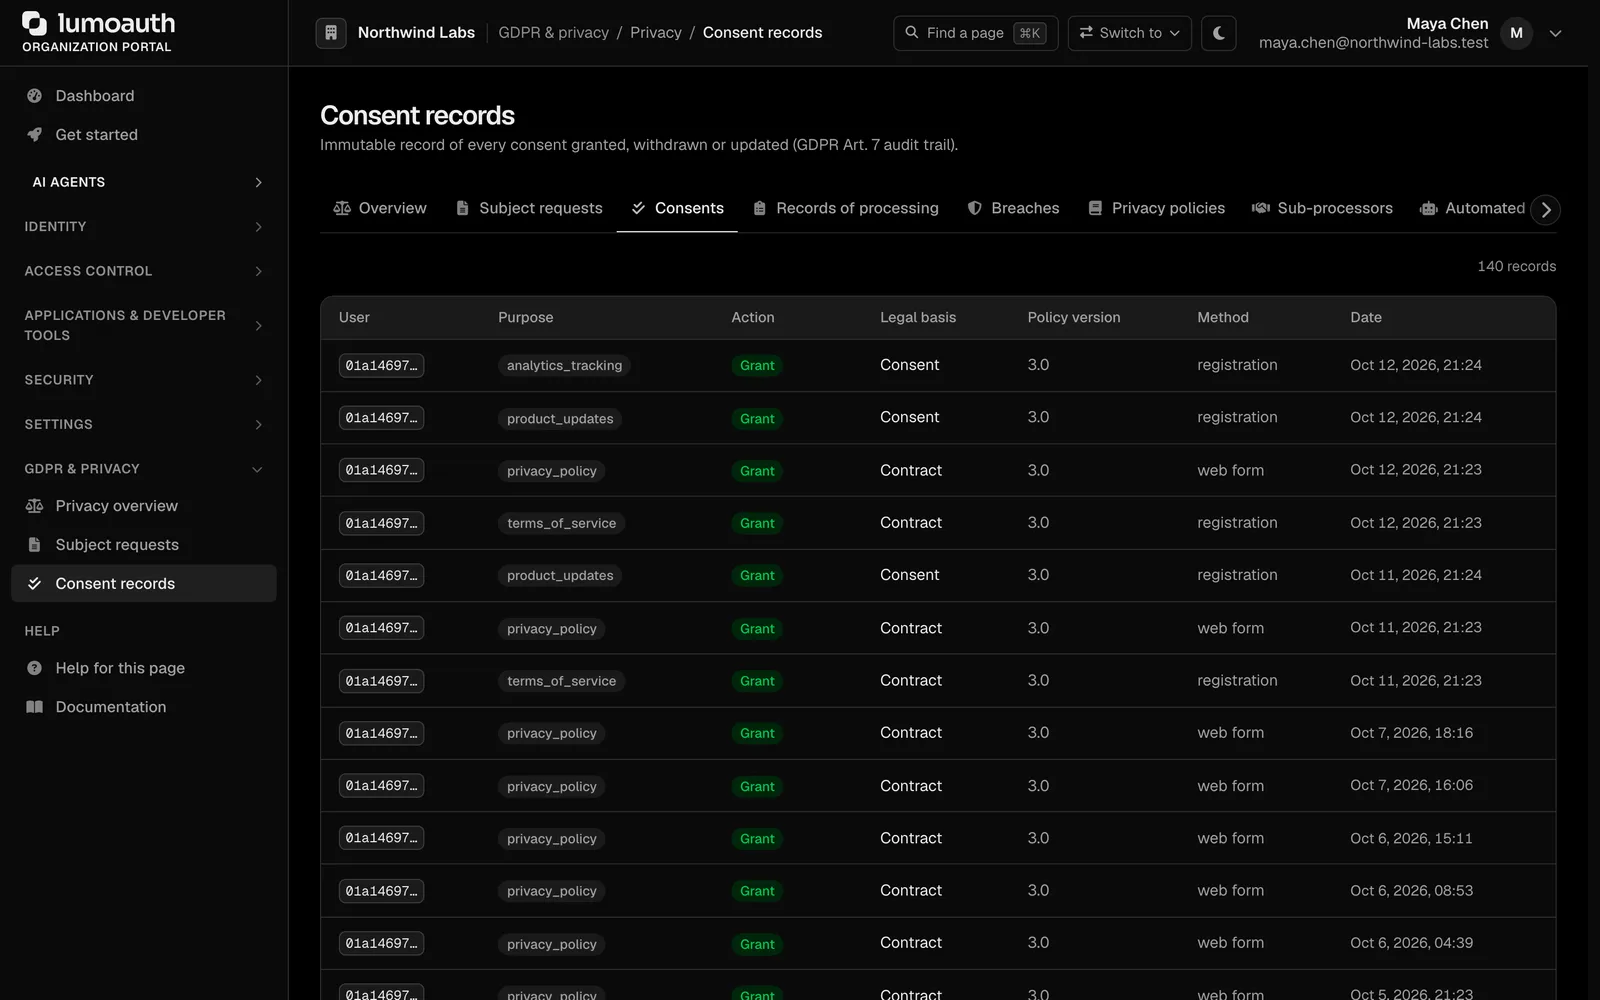
Records of processing and impact assessments
Keep the ROPA current and run DPIAs with a residual-risk matrix. Docs
Breach notification
Log an incident, track the 72-hour clock, record who was notified and when. Docs
Sub-processors and data export
A sub-processor registry with advance notice, and a full export of your organization's data. Docs
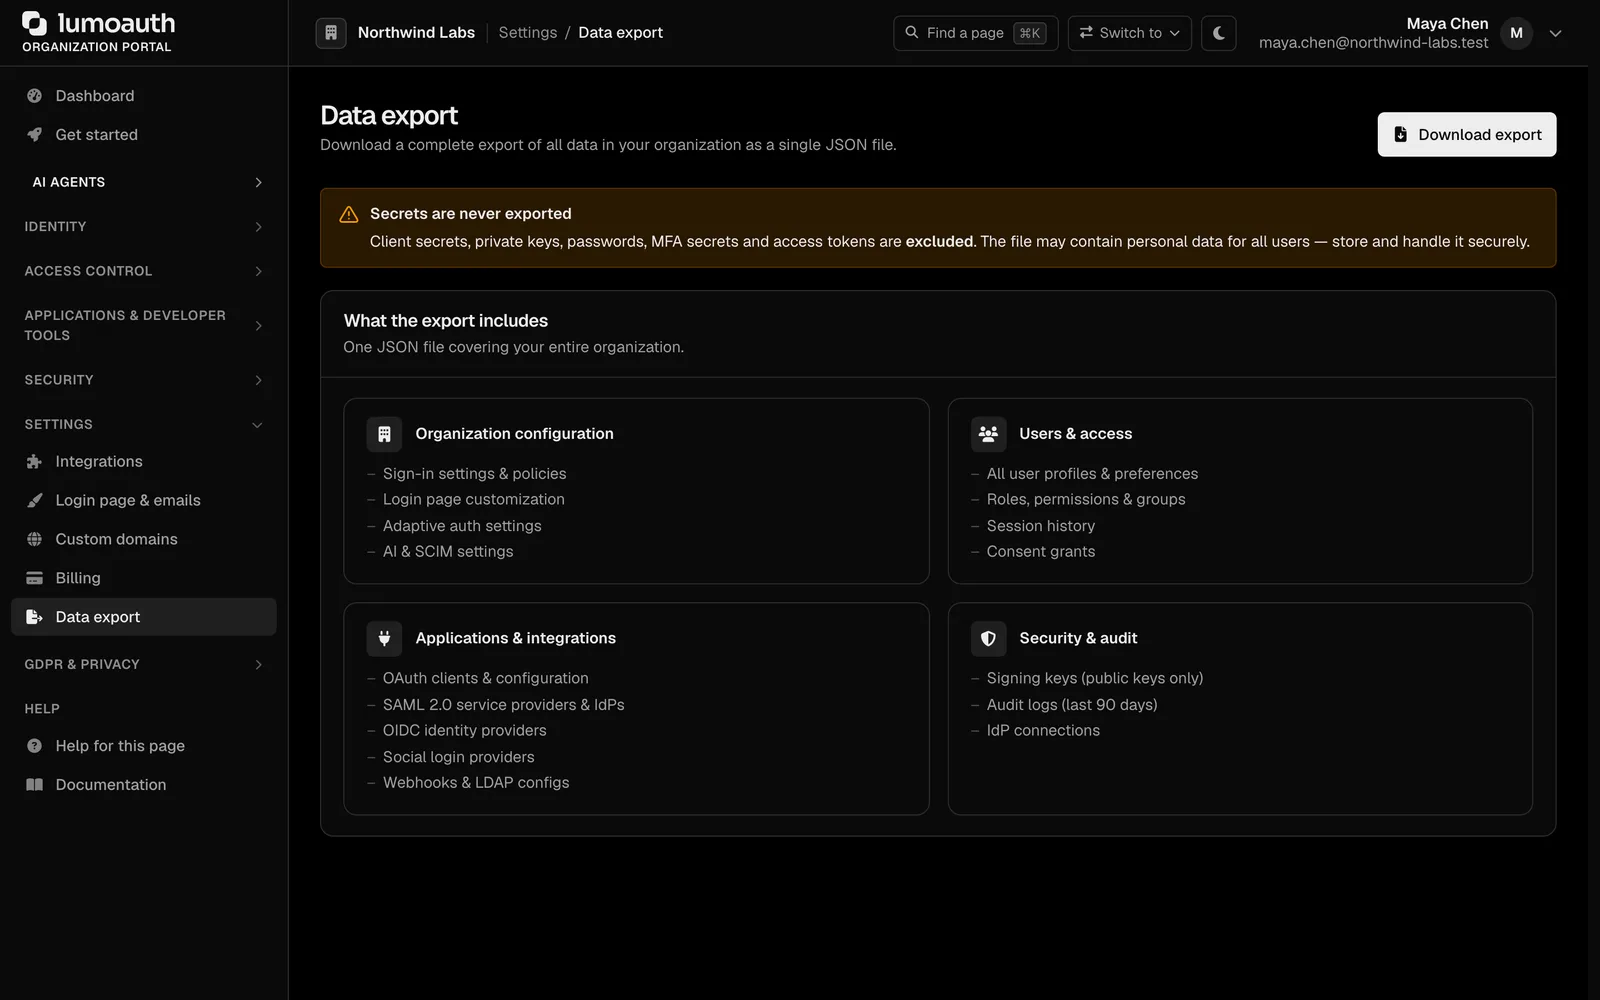
Evidence pack in one command
Build the audit evidence pack from the CLI when the auditor asks. Docs
Setting it up
Set retention rules
How long to keep inactive accounts and logs.
Publish your consent texts
Versioned; users re-consent when they change.
Review the request queue weekly
Most requests complete automatically; the rest are a click.
Standards involved
Plain names on the left, the specification on the right. The full map is in the standards reference.
- GDPR
- Articles 8, 15 to 22, 30, 33, 34, 35
- Transfers
- SCCs module 2, UK addendum, Swiss FADP
Which plan you need
Consent records and data-subject requests are on every plan. The full suite (ROPA, DPIA, breach management, sub-processor registry) is on Business and in the Audit & Compliance add-on ($99/month) on Pro.
Documentation
Questions
Where is data hosted?
Is there a signed DPA?
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.