Directory sync and provisioning
Provisioning by hand is how former employees keep access. LumoAuth receives users and groups from identity providers over SCIM, pulls joiners, movers and leavers from HR systems, and pushes changes out to downstream applications.
Manual onboarding is slow; manual offboarding is dangerous
A new hire waits days for accounts. A departure is handled by a ticket that someone closes next week. In between, access drifts away from what the org chart says.
How LumoAuth solves it
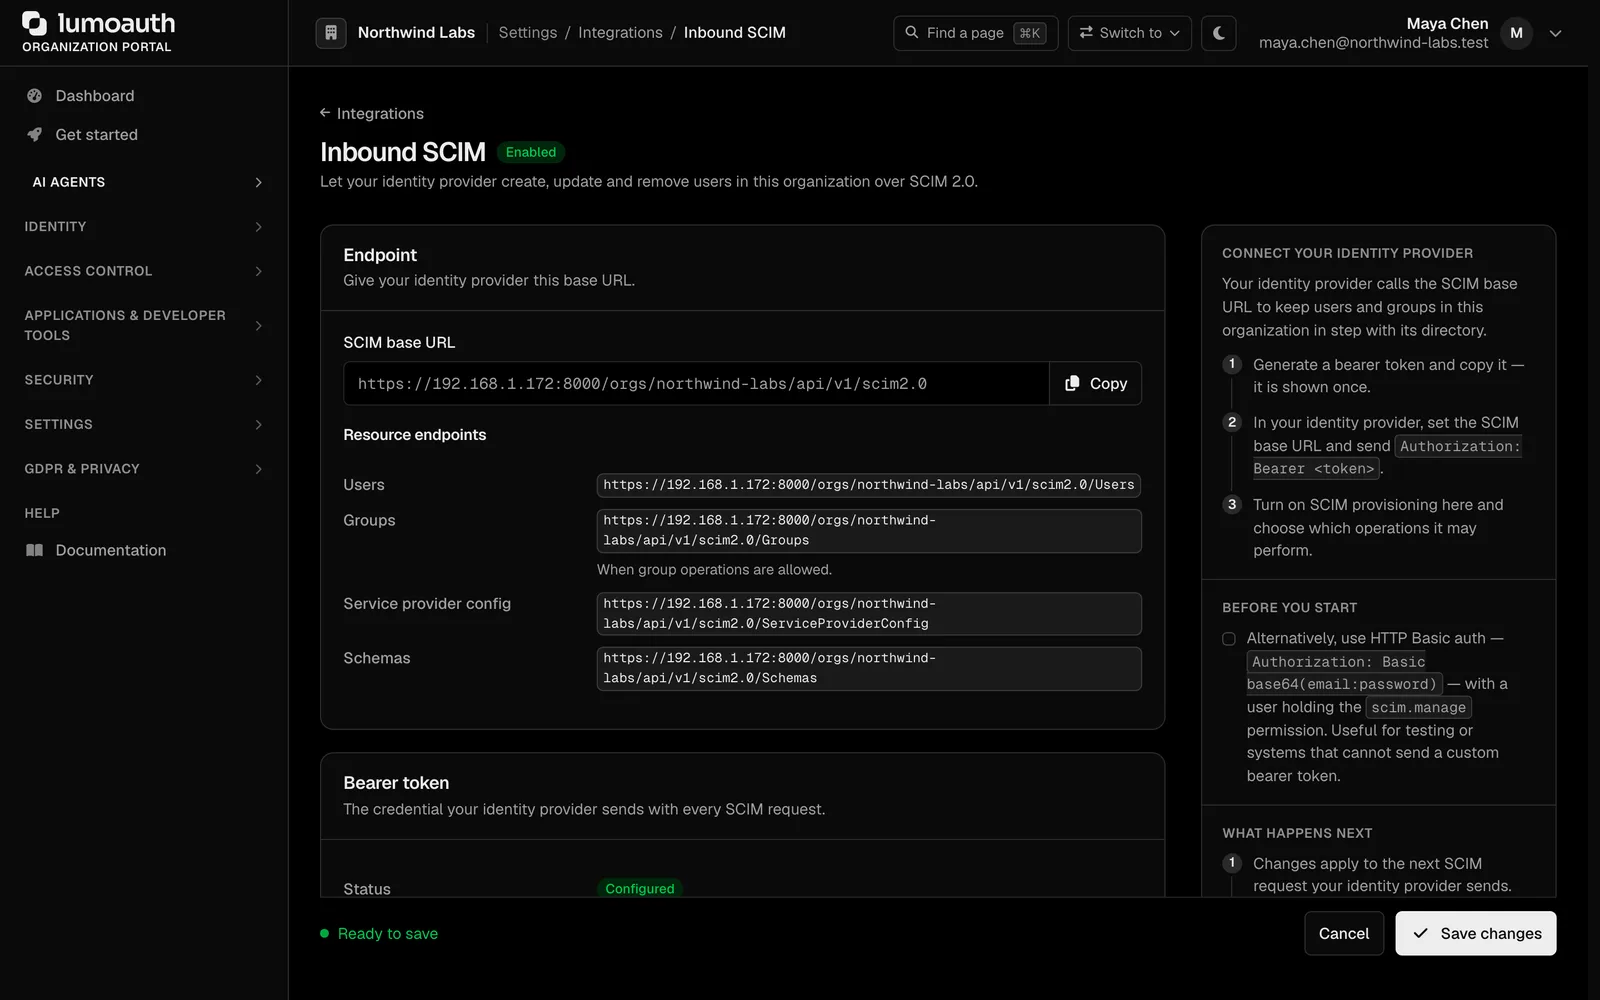
Inbound SCIM
Okta, Entra, OneLogin, JumpCloud and any SCIM 2.0 client create, update and deactivate users and groups. Patch, bulk and search are supported. Docs
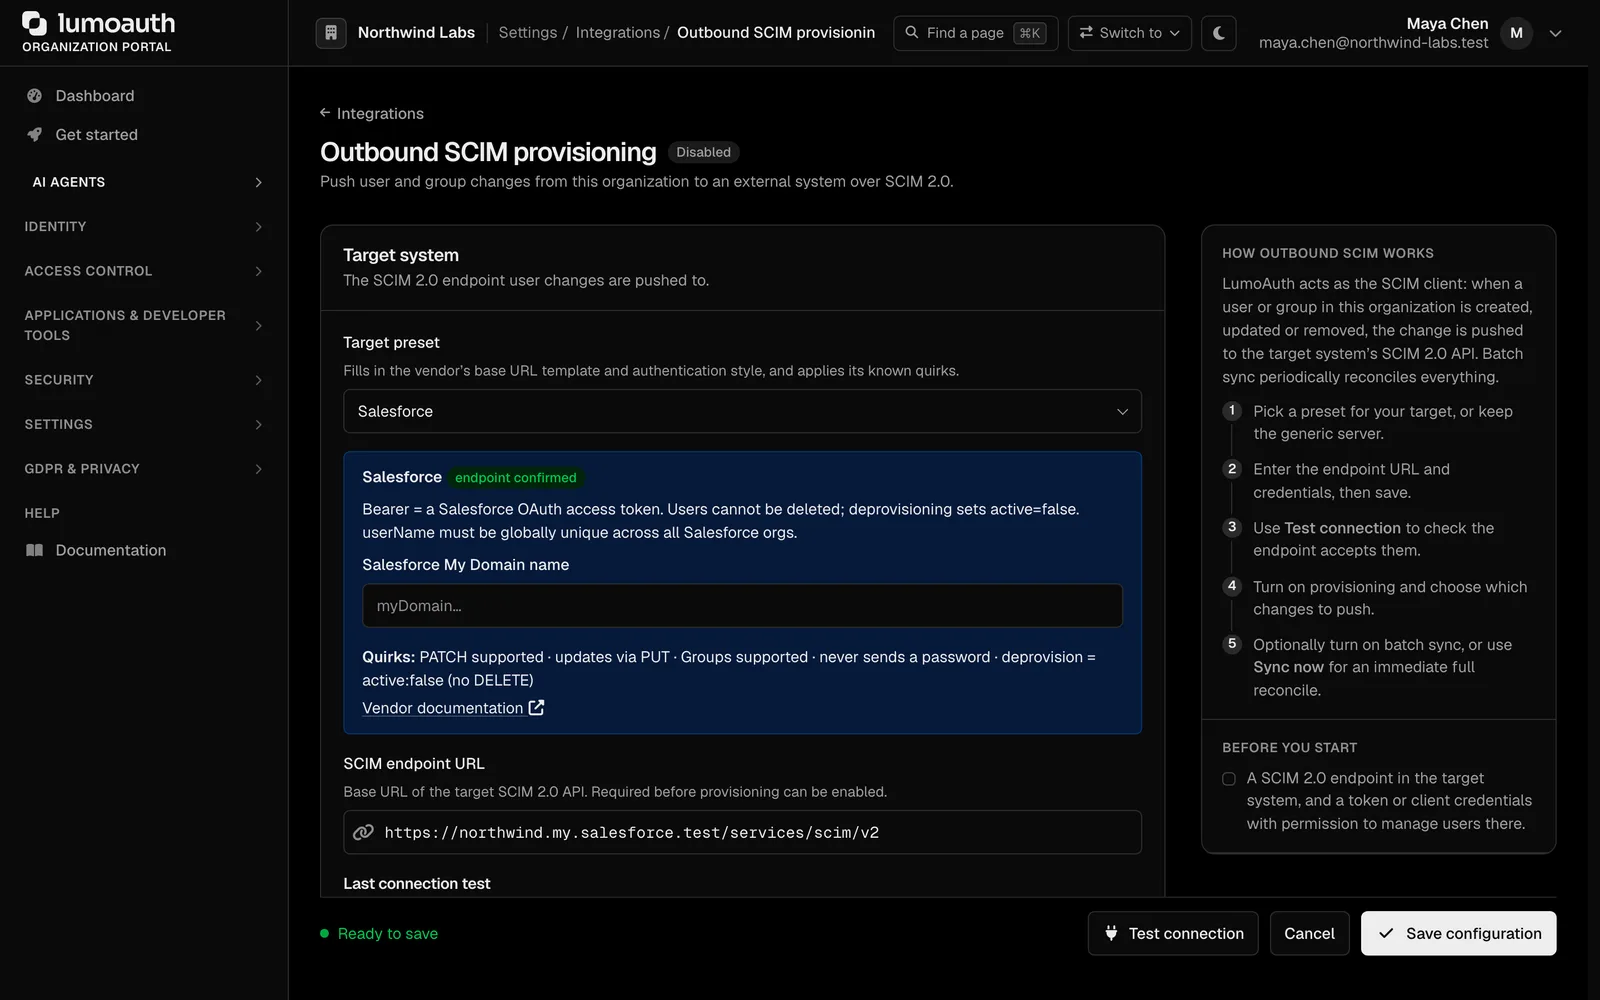
Outbound SCIM
Push users and groups to Okta, Entra, Google Workspace, Salesforce, GitHub, Slack, Zoom, Atlassian and others with presets that handle each vendor's quirks. Docs
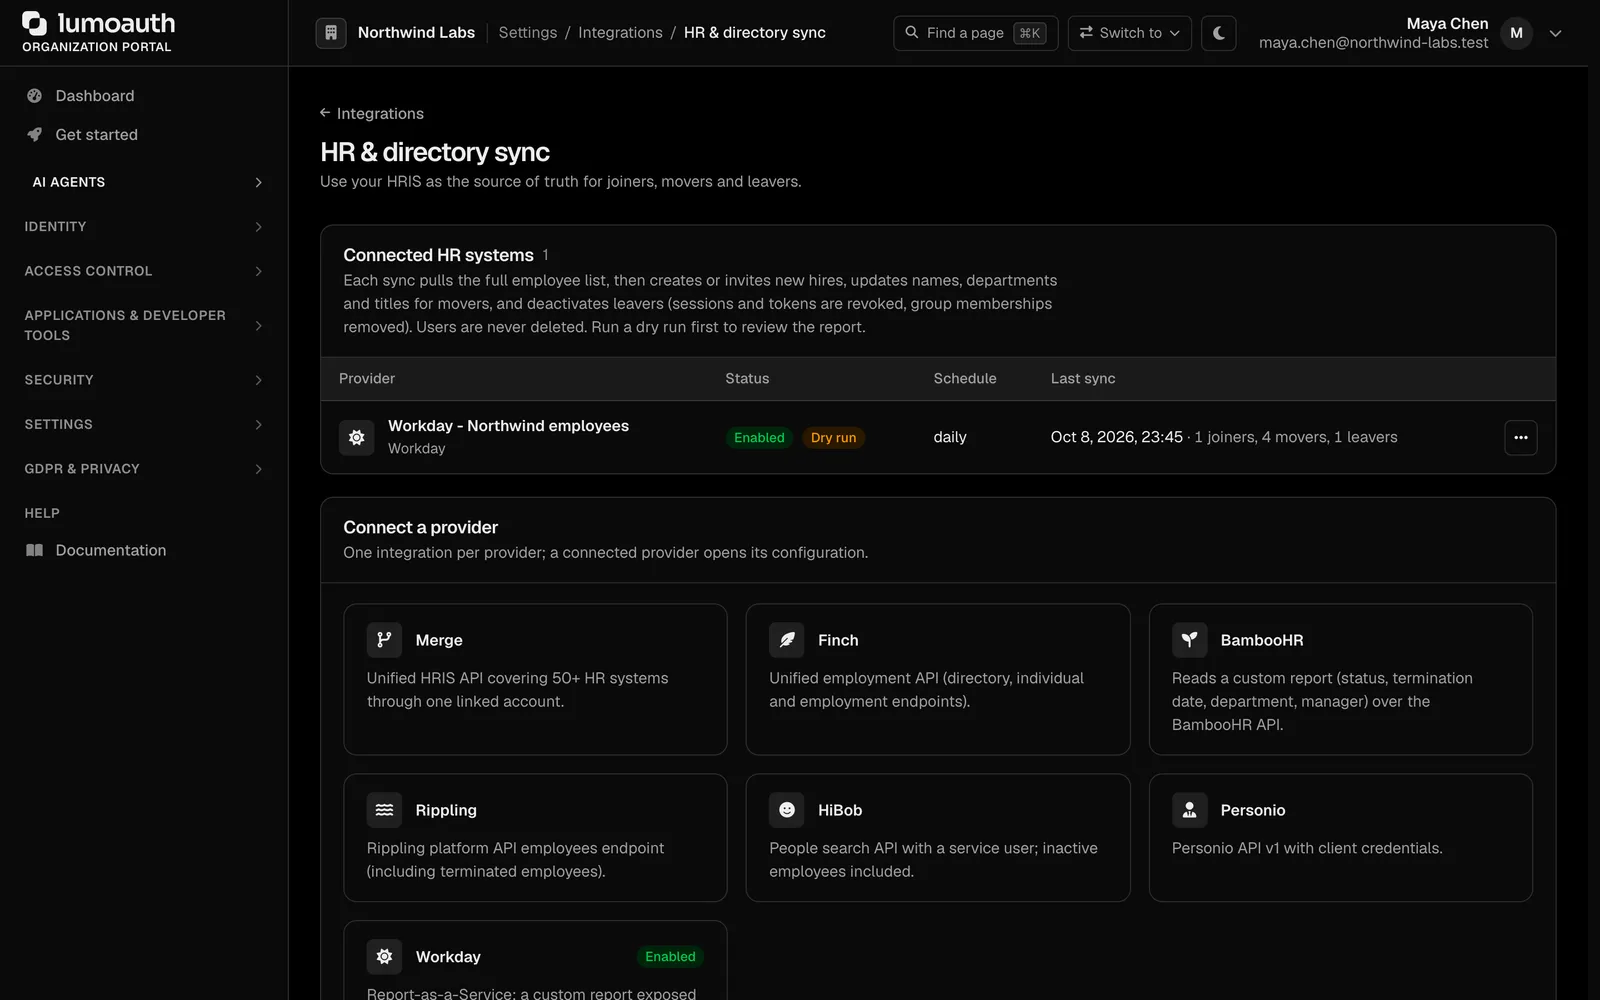
HR system as the source of truth
Connect BambooHR, Workday, Rippling, HiBob, Personio, Finch or Merge. Start dates create accounts, departures deactivate them, and department changes update groups. Docs
Groups to roles
A group in the directory maps to a role in your product, so access follows the org chart. Docs
Sessions end on deprovisioning
Deactivating a user revokes their sessions and tokens, and a security event tells downstream apps. Docs
Webhooks for everything else
User and group events can trigger your own onboarding steps. Docs
Setting it up
Create a SCIM token
Settings → Integrations → SCIM provisioning. Copy the endpoint and token into the identity provider.
Choose provisioning behaviour
Default roles for new users, whether deletes deactivate or remove, and which attributes map to your profile fields.
Add outbound targets
Pick a preset, add credentials, choose whether to sync on login, on change or on a schedule.
Watch the audit log
Every provisioning call is logged, so a wrong mapping is easy to find.
Standards involved
Plain names on the left, the specification on the right. The full map is in the standards reference.
- SCIM 2.0
- RFC 7642, RFC 7643, RFC 7644
- SCIM notifications
- SCIM Notify draft
- Security events
- OpenID SSF and CAEP
Which plan you need
Inbound SCIM is on every plan. Outbound SCIM and HR system sync are on the Business plan.
Documentation
Questions
Which identity providers can push to LumoAuth?
What happens to a deprovisioned user's data?
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.