Key management and bring-your-own keys
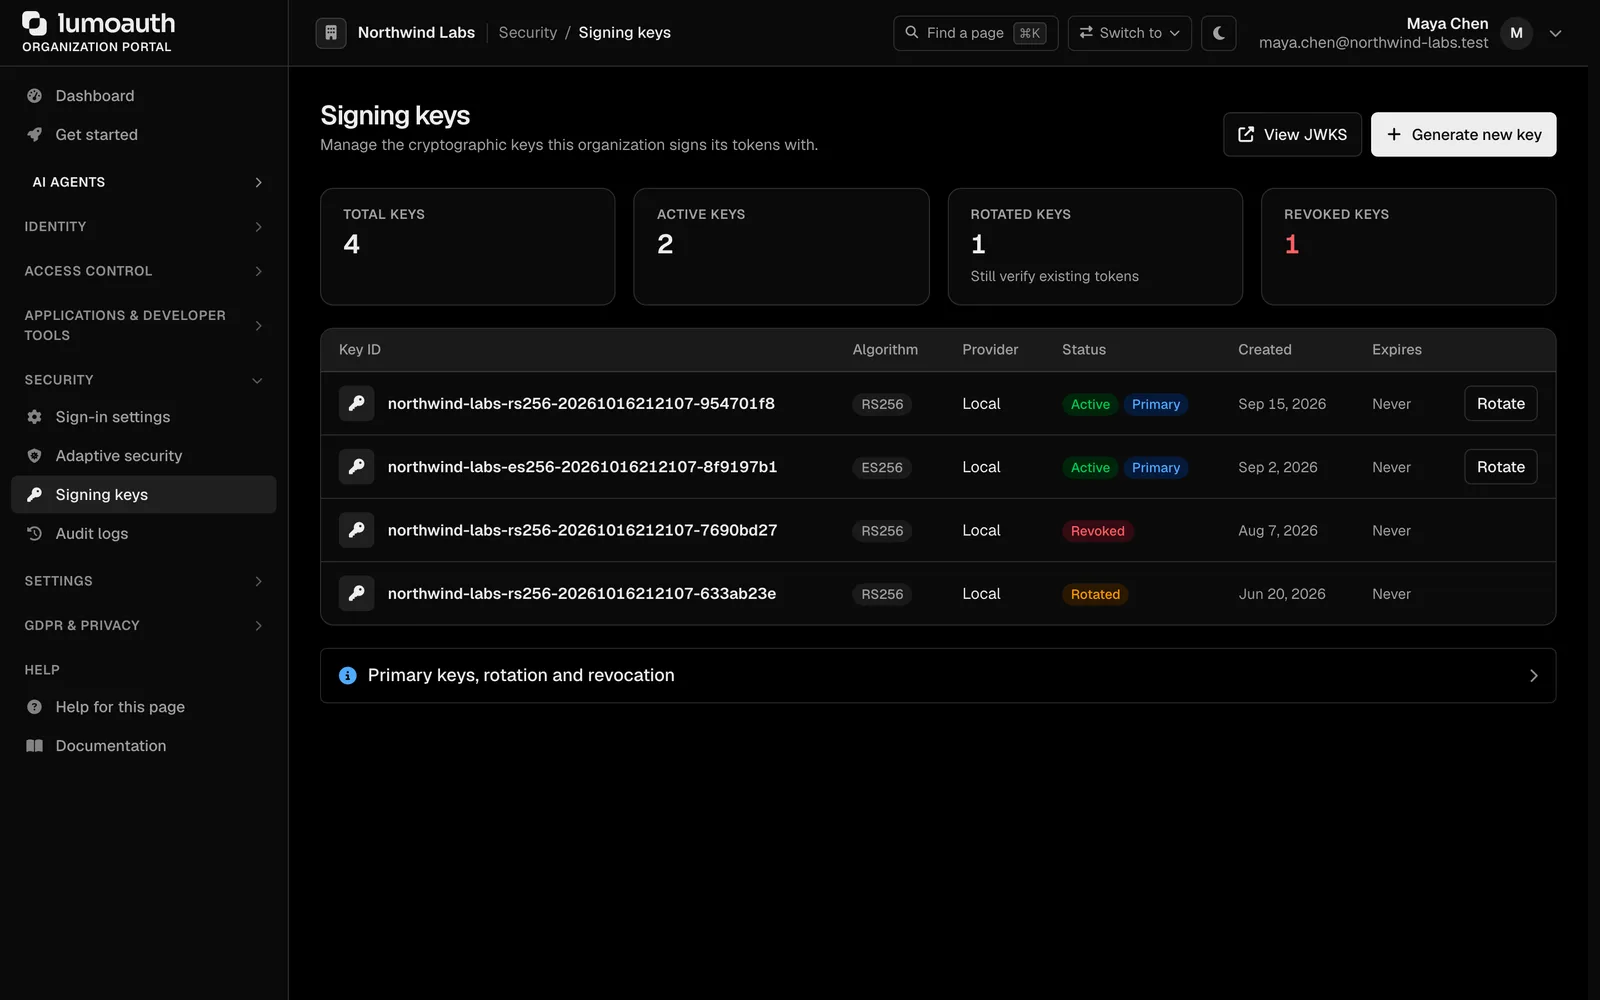
Every organization has its own signing keys, published as a standard key set. You can rotate them from the portal with an overlap period, and you can generate them inside your own key management service so the private key never exists anywhere else.
Shared keys and manual rotation
Many providers sign every customer's tokens with the same key and make rotation an incident. Regulated customers want the key under their control.
How LumoAuth solves it
Per-organization keys
Each organization signs its own tokens; a compromise does not cross customers. Docs
Rotation without downtime
Generate the next key, promote it, keep the old one published until tokens expire. Docs
Fifteen key providers
Local, AWS KMS and CloudHSM, Azure Key Vault and Managed HSM, Google Cloud KMS, HashiCorp Vault, OpenBao, Akeyless, Thales CipherTrust, Fortanix DSM, Entrust KeyControl, Oracle OCI Vault, IBM Key Protect and any PKCS#11 device through a sidecar. Docs
Only public keys stored
Private keys are generated inside the provider and never imported. Losing provider access stops signing; it never exposes the key. Docs
Health checks
The certificate and key check command validates every platform key and trust anchor, with expiry warnings. Docs
Setting it up
Choose a provider when generating a key
Security → Signing keys → Generate.
Validate
The form checks the credentials and the key policy before saving.
Promote and rotate on your schedule
Standards involved
Plain names on the left, the specification on the right. The full map is in the standards reference.
- Key sets
- RFC 7517 JWKS, RFC 7638 thumbprints
- HSM access
- PKCS#11, FIPS 140-3 Level 3 devices supported
Which plan you need
Per-organization keys and rotation are on every plan. External KMS and HSM providers are the Bring-your-own signing keys add-on ($299/month) on Business.
Documentation
Questions
Can I use my KMS for encrypting secrets too?
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.