Workforce identity
Internal tools deserve the same sign-in as customer-facing ones. LumoAuth signs staff in with passkeys or the company identity provider, provisions them from the HR system, scopes access with groups and roles, and makes privileged access something you request rather than something you keep.
Internal tools accumulate permanent admin access
Engineers get production access for one incident and keep it for years. Contractors leave and their accounts stay. Nobody can say who can see what.
How LumoAuth solves it
Phishing-resistant sign-in for staff
Require passkeys for everyone, or for admins only. Docs
Onboard from HR
Accounts appear on the start date and disappear on the end date, from BambooHR, Workday, Rippling, HiBob, Personio, Finch or Merge. Docs
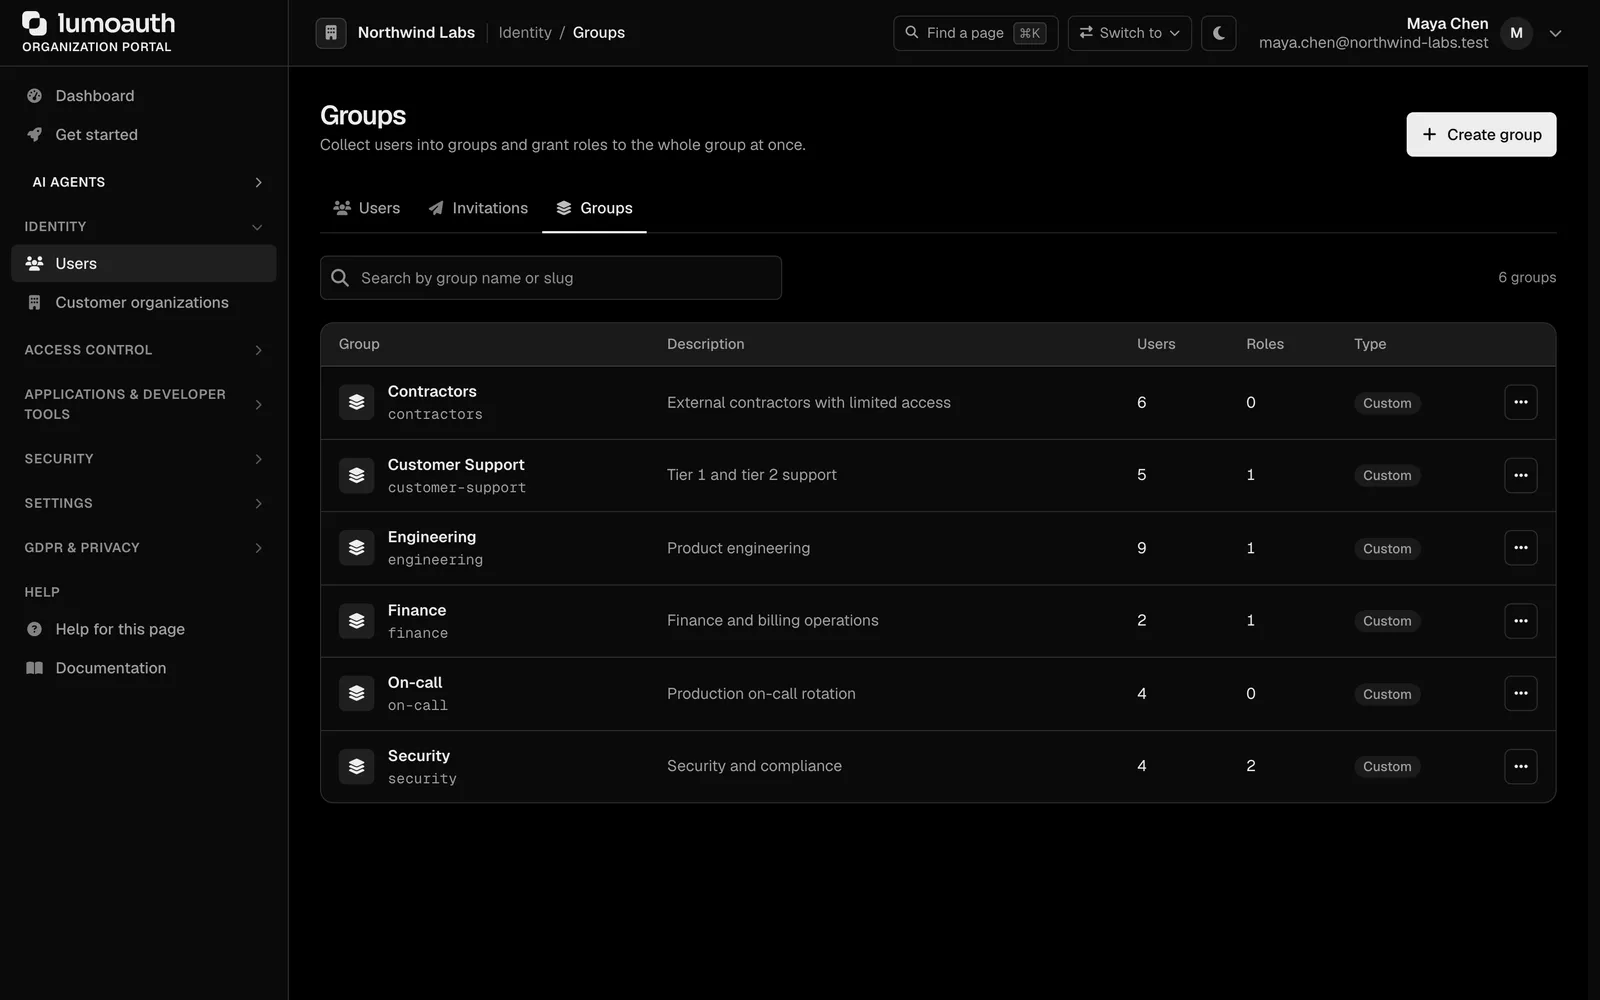
Groups and roles
Department groups map to roles in each internal tool. Docs
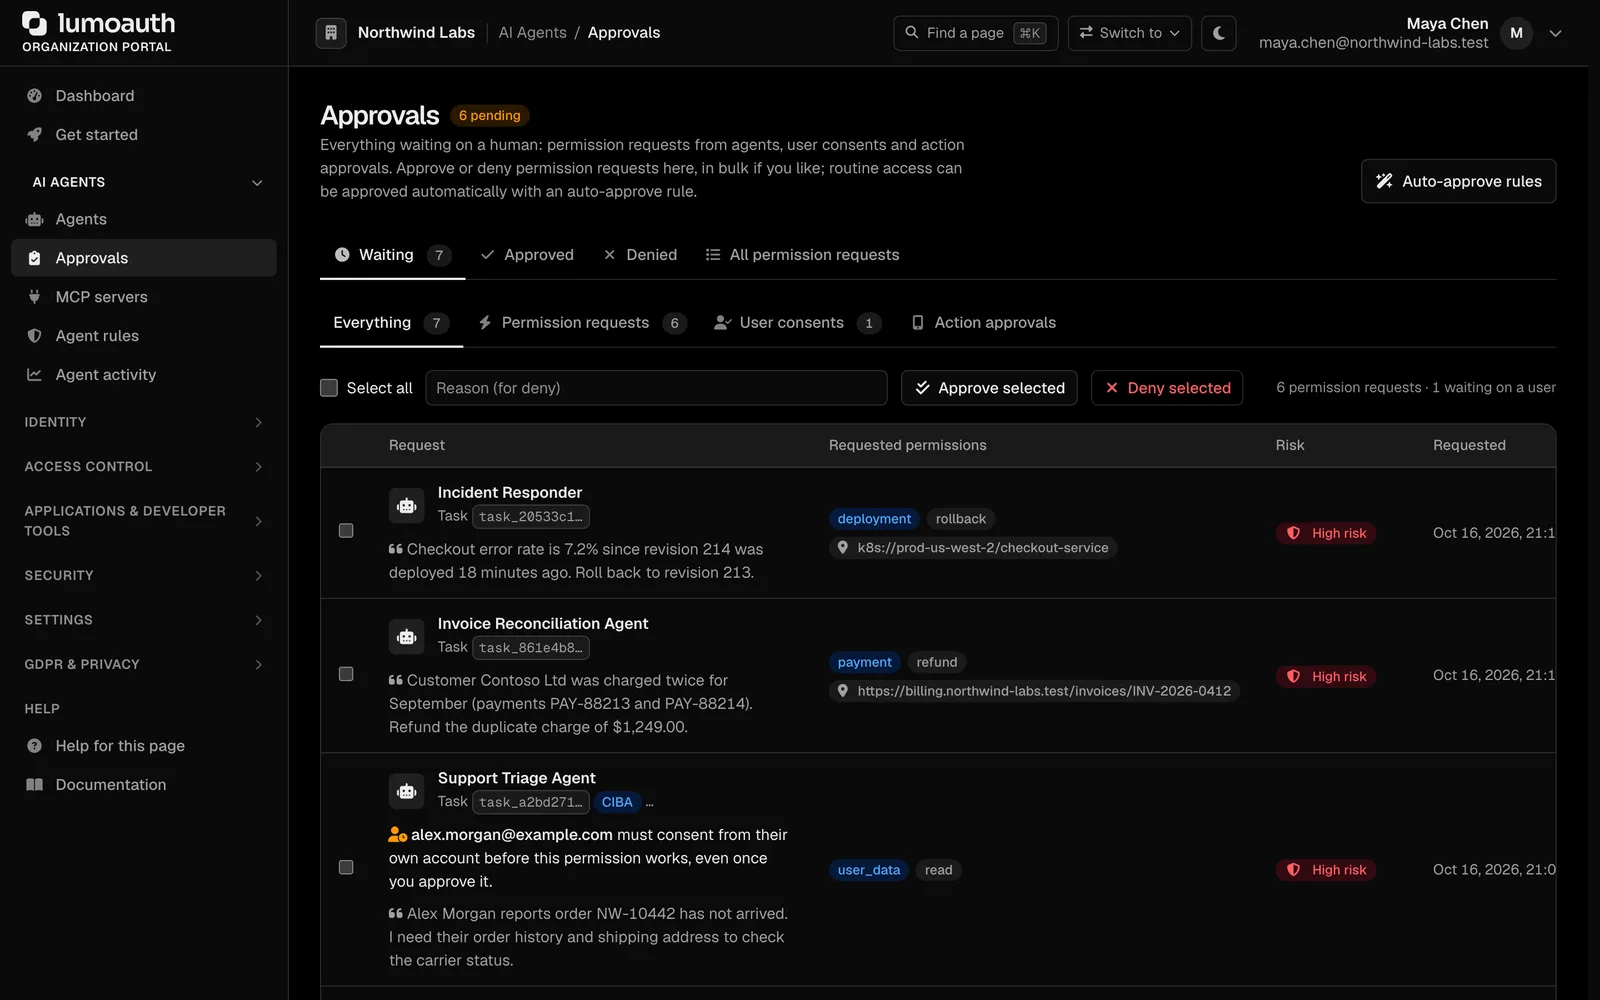
Time-bound privileged access
An engineer requests production access with a reason; an approver grants it for an hour; it ends on its own. Same inbox as agent approvals. Docs
Device trust
Allow sign-in only from managed, healthy devices using CrowdStrike, Intune, Jamf or Kandji. Docs

SSO for the portal itself
Your admins sign into the LumoAuth portal with your identity provider. Docs
Setting it up
Connect the identity provider or require passkeys
Connect the HR system
Map departments to groups.
Register internal tools as applications
Each one gets an OpenID Connect client; protect routes with the SDK middleware.
Replace standing admin access with requests
Approvers get a notification; grants expire.
Standards involved
Plain names on the left, the specification on the right. The full map is in the standards reference.
- Passkeys
- WebAuthn, FIDO2
- Provisioning
- SCIM 2.0
- Sign-in
- OpenID Connect, SAML 2.0
Which plan you need
Passkeys, groups and roles are on every plan. HR sync, device posture and admin SSO are on Business. Time-bound access through just-in-time requests needs the Agent Governance add-on on Pro or the Business plan.
Documentation
Questions
Can I replace service accounts too?
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.