Identity providers
Enterprise sign-in connections are configured per organization under Settings → Integrations. Presets fill in the right endpoints and attribute mappings for the providers most customers use; any other SAML or OpenID Connect provider works from its metadata.
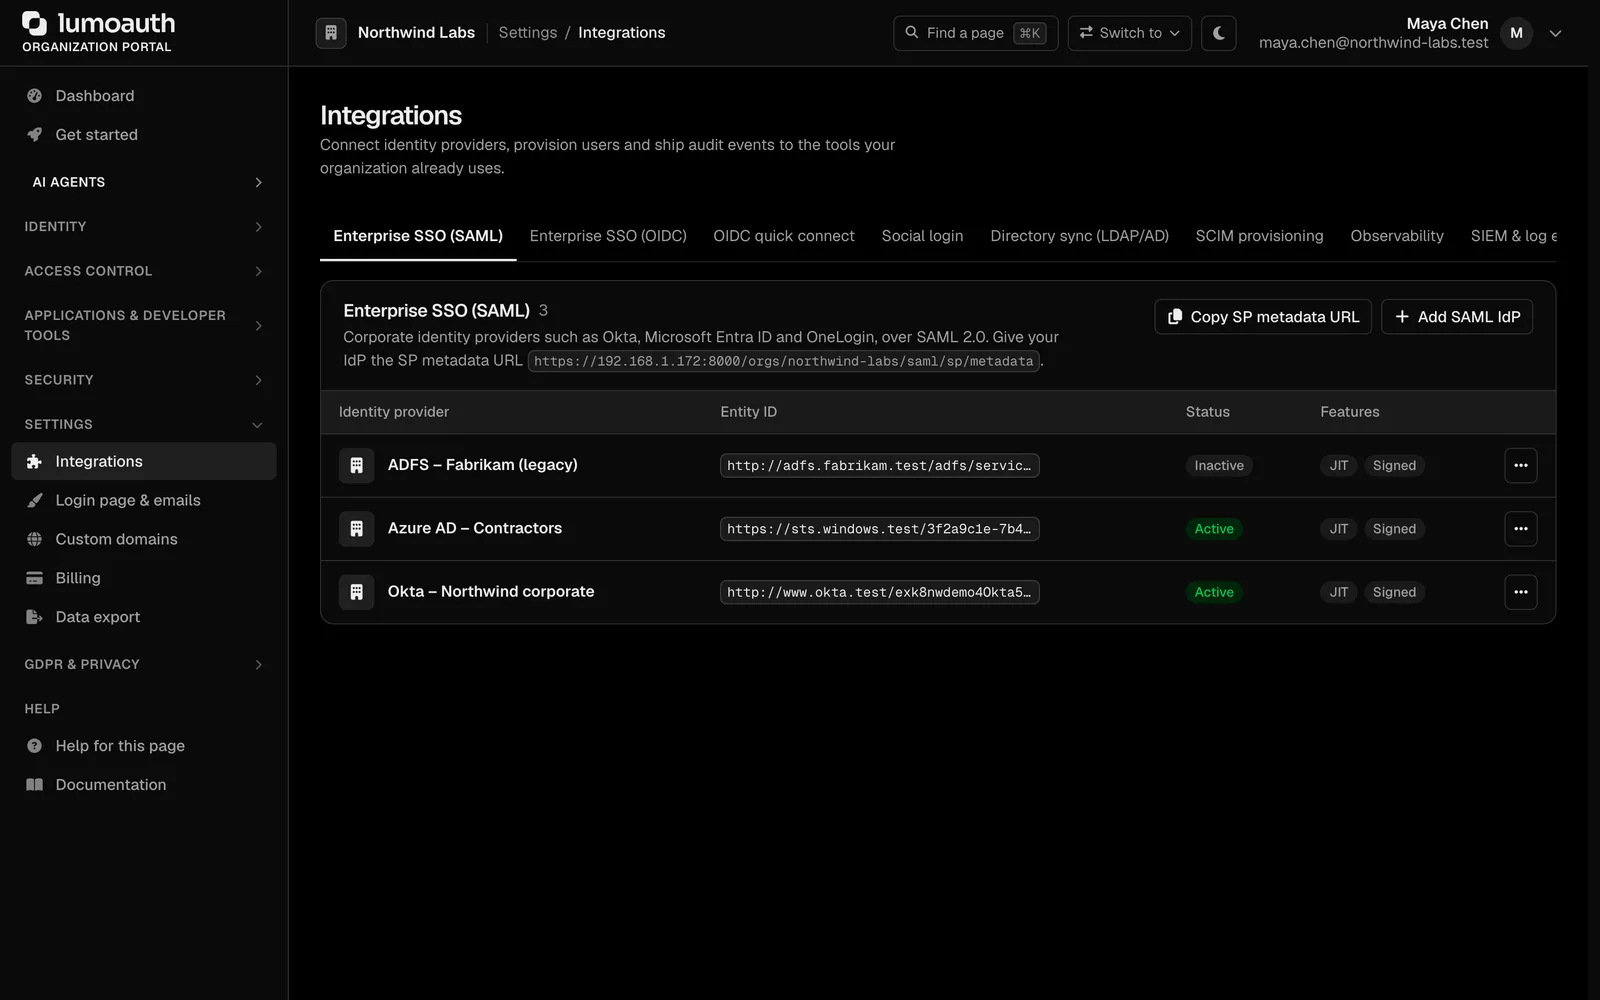
What connects
SAML and OpenID Connect presets
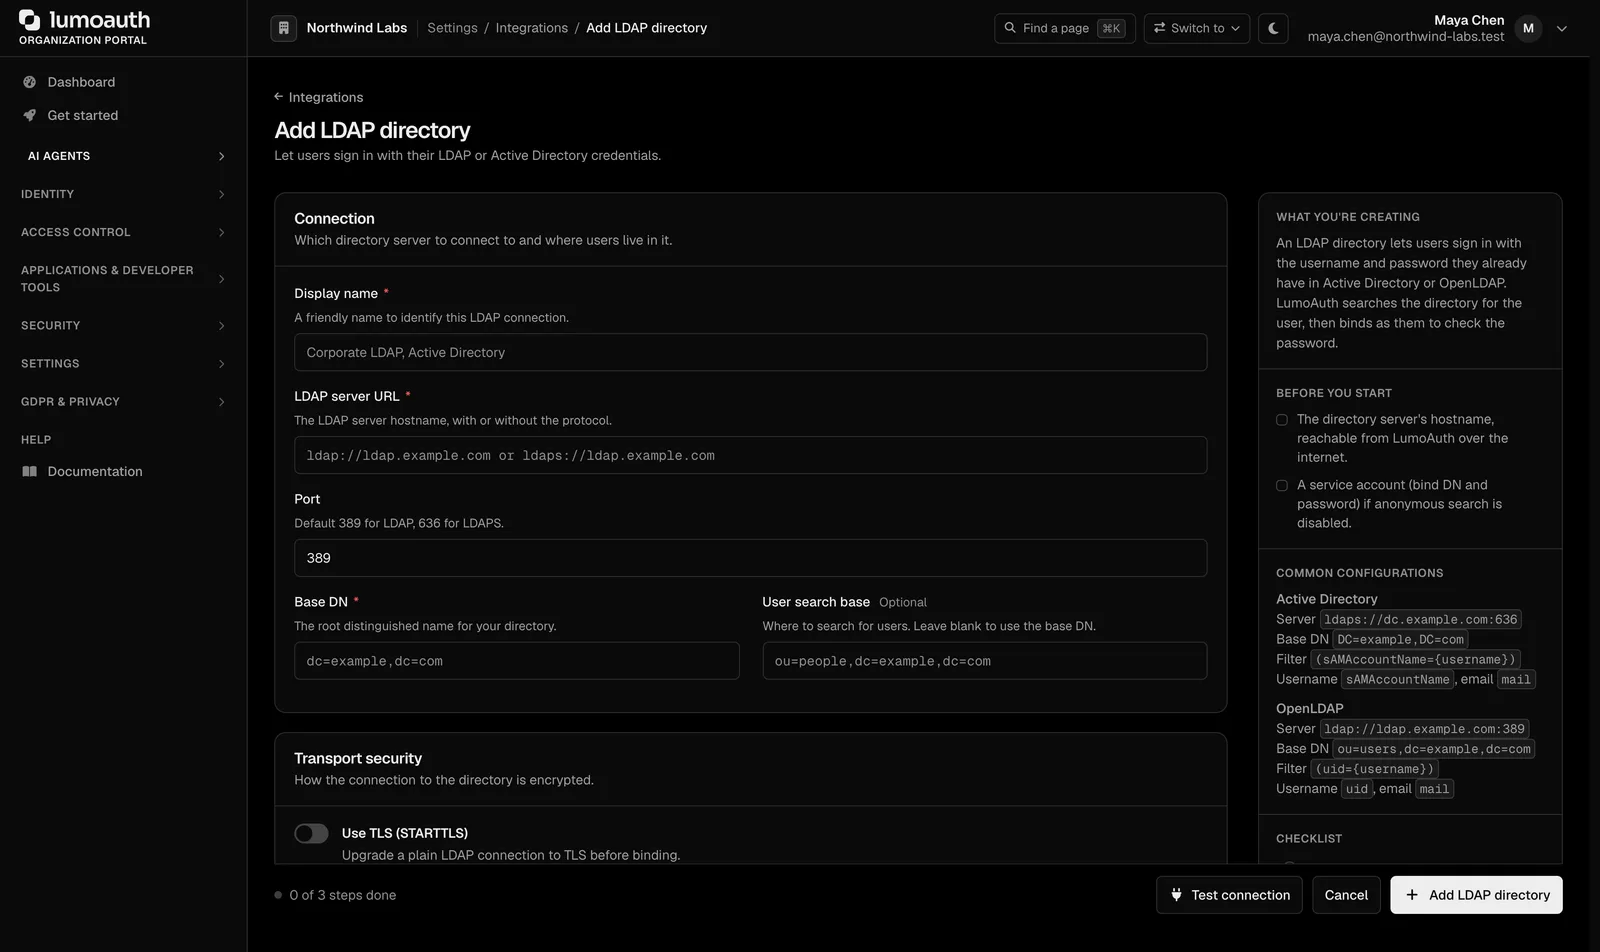
Directories
Marketplace listings documented
How LumoAuth solves it
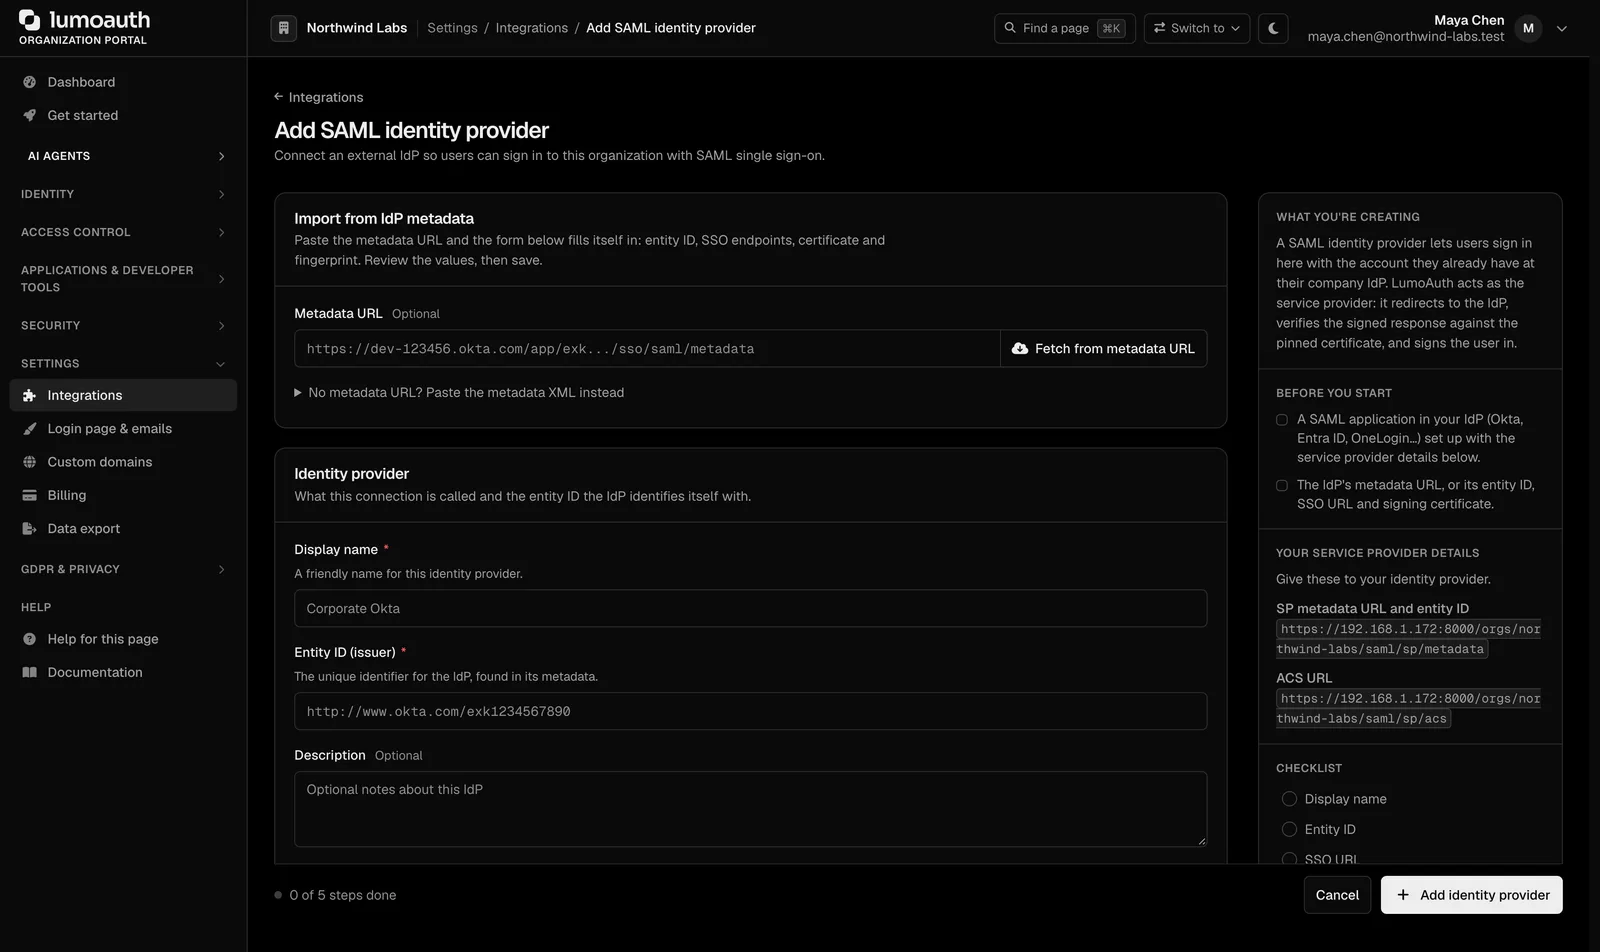
Inbound SAML
Paste the provider's metadata, choose the NameID format and signing options, map attributes. Docs
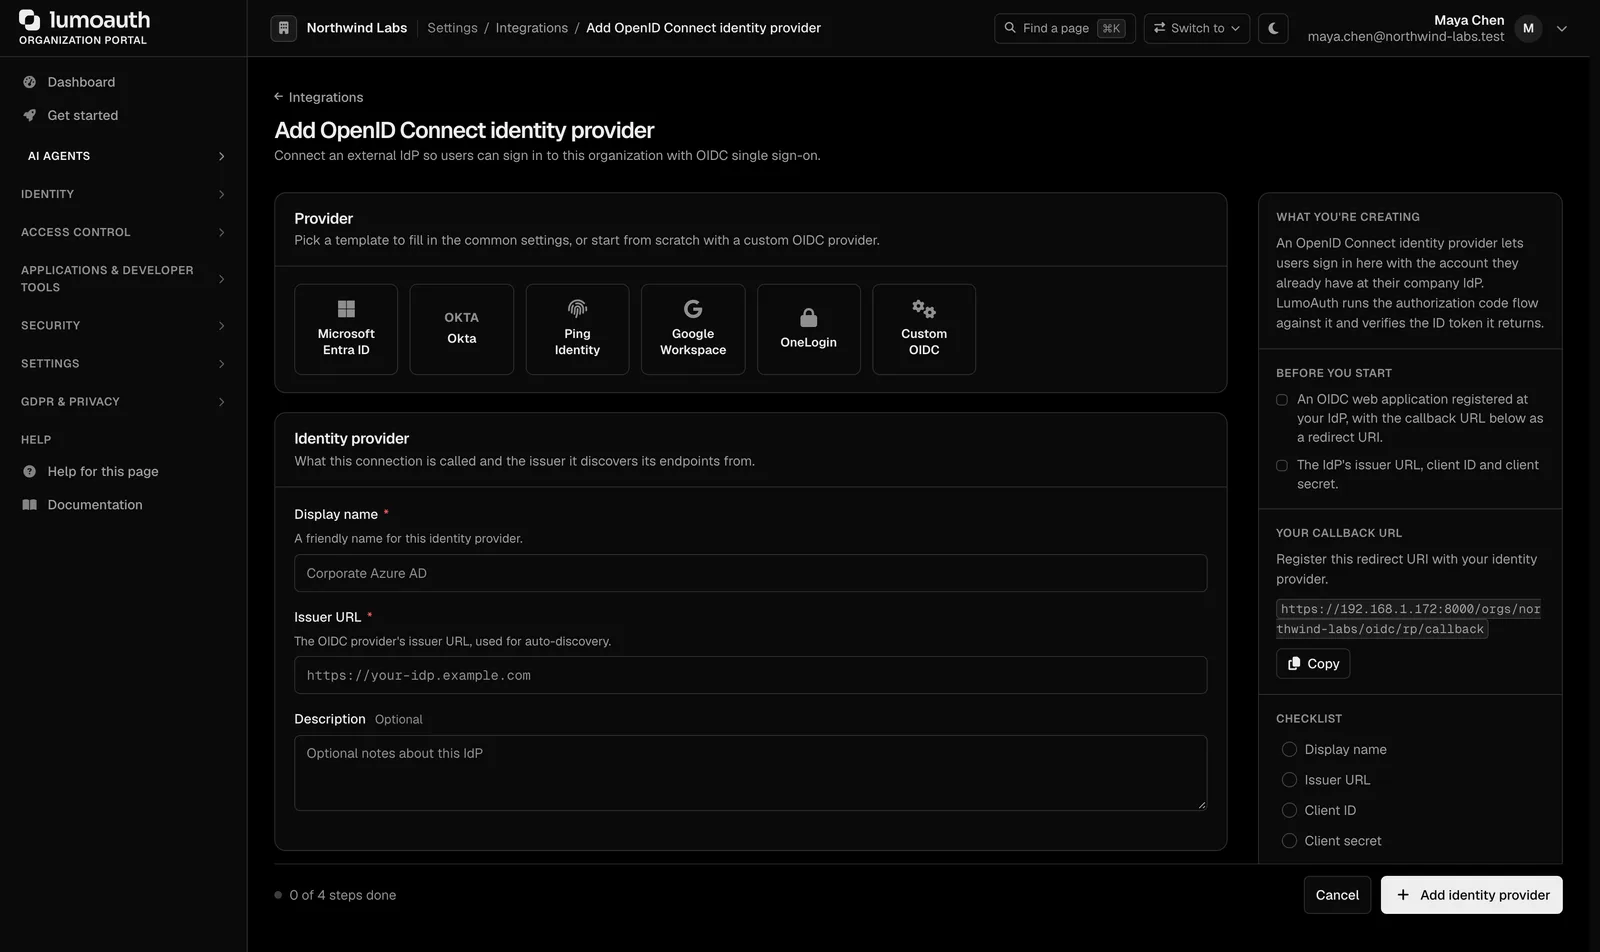
Inbound OpenID Connect
Enter the discovery URL and client credentials; claims map to roles and groups. Docs
Outbound: LumoAuth as the identity provider
Sign users into SAML-only applications. Docs
Which plan you need
One enterprise connection on Developer and Pro, ten on Business with per-connection overage. LDAP is on Business. Acting as a SAML identity provider is an add-on on Pro and included in Business.
Documentation
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.