Solutions
Integration
SIEM and log export
Log sinks ship every audit event asynchronously, with retries, to one or more destinations. Events carry actor, target, IP, geography, risk and a trace ID; the S3 and generic HTTPS sinks use the OCSF schema.
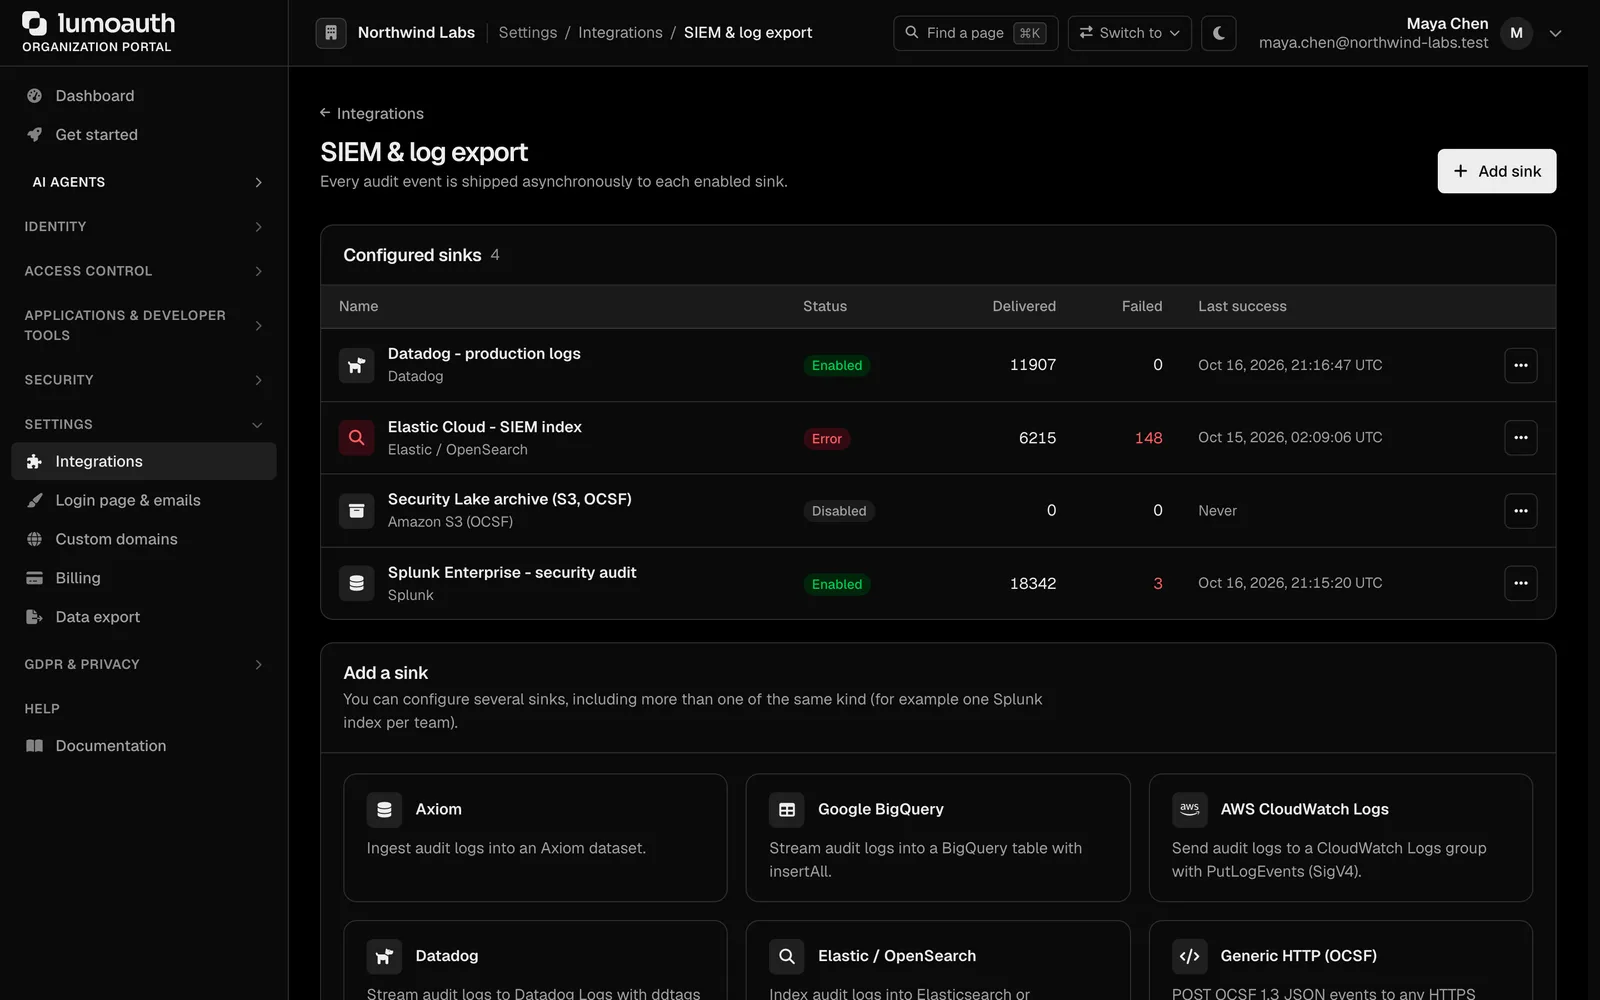
What connects
Security tools
SPSplunk
MIMicrosoft Sentinel
GOGoogle SecOps
ELElastic and OpenSearch
SUSumo Logic
AWAWS CloudWatch Logs
Observability
DADatadog
AXAxiom
HOHoneycomb
OPOpenTelemetry (OTLP)
Storage and warehouses
AMAmazon S3 (OCSF)
GOGoogle BigQuery
SNSnowflake
ANAny HTTPS endpoint (OCSF)
How LumoAuth solves it
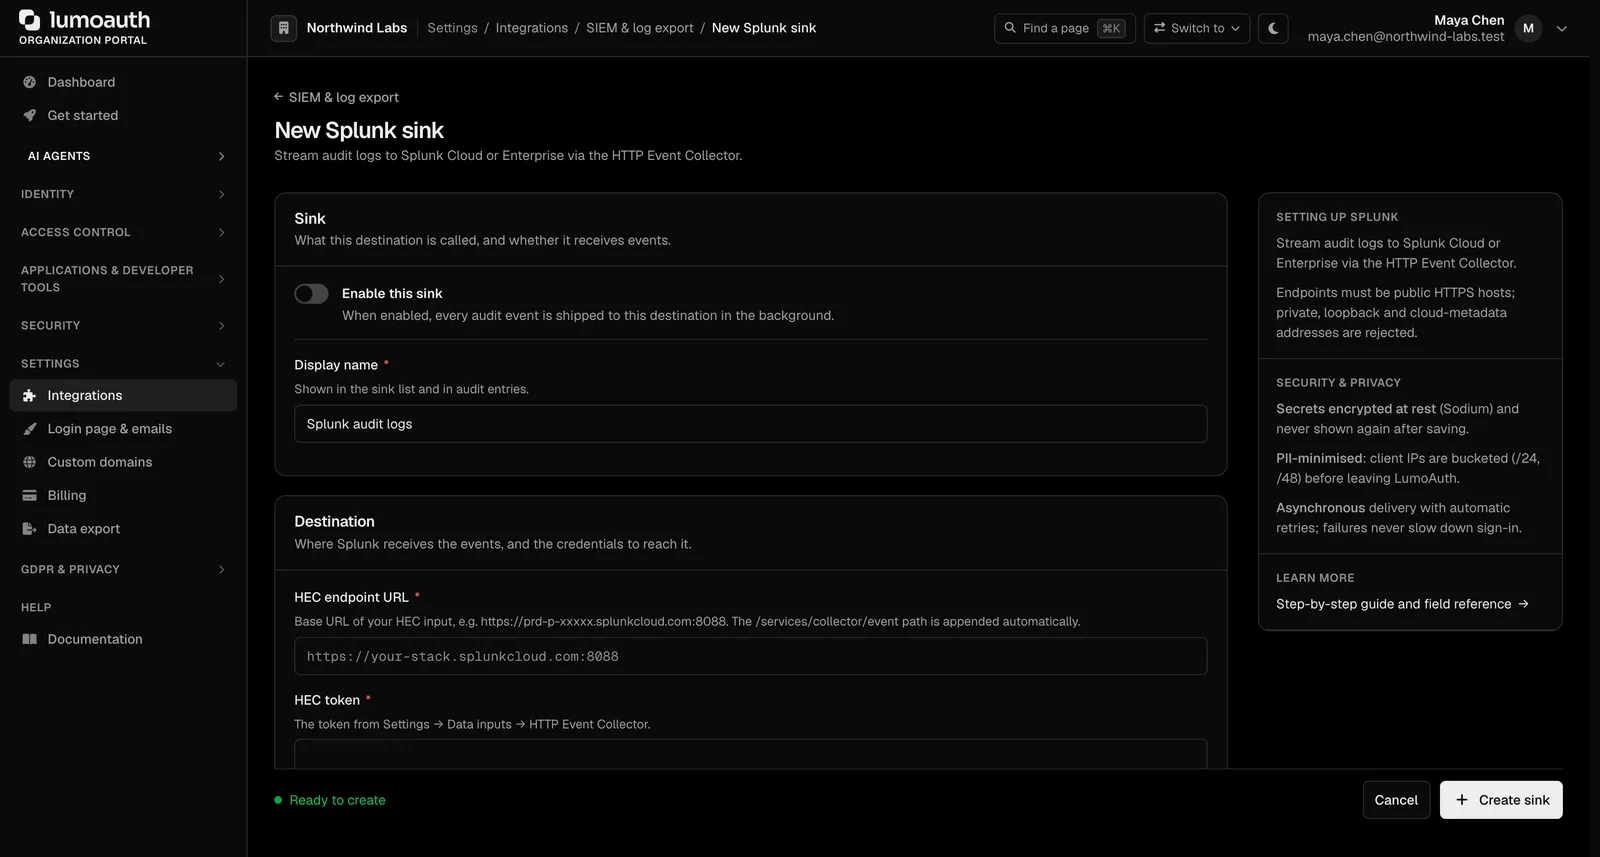
Which plan you need
One log stream is included on Business; more at $99/month each. On Pro, log streaming comes with the Audit & Compliance add-on.
Documentation
Ship passwordless sign-in this week. Put guardrails on your agents today.
The Developer plan is free for 10,000 monthly users and ten agents, with no card. Everything speaks open standards, so moving in or out is a config change.